

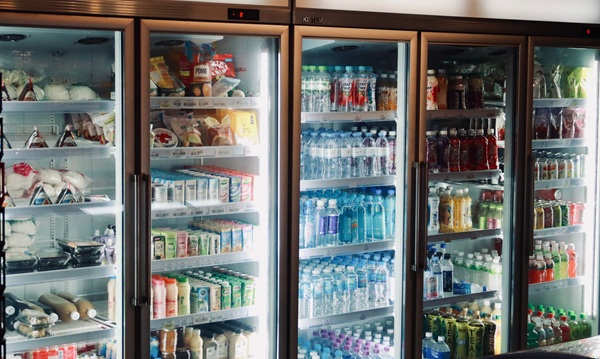
Hackers took control of refrigeration systems at hundreds of French supermarkets overnight on Oct. 11, turning refrigerators and freezers into heaters. Temperatures in some units climbed as high as 122 degrees Fahrenheit (50 degrees Celsius), according to cybersecurity firm Finite State. The attack spoiled fresh and frozen food and reportedly caused fires at several stores, Reuters reported. At least 350 supermarkets were affected, including locations operated by Carrefour, Intermarché, Monoprix, and Coopérative U.
The attackers reportedly manipulated the equipment's built-in defrost function, which normally melts ice that accumulates on refrigeration coils. French authorities are investigating the attacks but have not established how the hackers initially gained access to the controllers.
In a separate experiment, cybersecurity firm Finite State used an AI-driven workflow to independently rediscover two known vulnerabilities in Danfoss refrigeration-controller firmware within hours. The findings suggest that AI could dramatically accelerate vulnerability discovery, even as businesses struggle to patch or replace equipment that may remain in service for decades.
Known Vulnerabilities Leave Refrigeration Controllers Exposed
Researchers had identified security weaknesses in Danfoss refrigeration controllers well before the French attacks. In August 2026, cybersecurity firm Claroty publicly detailed vulnerabilities in the company's AK-SM 800A controllers that could allow attackers to bypass authentication and execute malicious commands. Danfoss had released firmware fixes in 2025, but some systems were still running outdated versions.
Some equipment was too old to patch. Danfoss had discontinued support for its AK-SM 800 and AK-SC 355 controllers, leaving operators with little choice but to replace the hardware or isolate it from potential attackers. The French attacks affected refrigeration equipment from multiple manufacturers, however, and investigators have not established whether the vulnerabilities identified by Claroty played a role.
Internet exposure compounded the risks. On October 13, two days after the attacks, Reuters identified at least 4,500 Danfoss refrigeration-controller interfaces accessible through the public internet using the search engine Shodan. While exposure doesn't necessarily mean a controller is vulnerable, it can give attackers a way to reach equipment that was never intended to be directly accessible online.
According to Danfoss, similar attacks targeted 16 supermarkets in Russia and 40 stores in Israel in 2022. Those incidents involved older refrigeration controllers, with affected Israeli stores lacking adequate firewall or VPN protection.
“This continues an alarming trend, which is using cyber-attacks not for data theft but to create physical kinetic damage by exploiting OT/IoT devices,” said John Gallagher, vice president at Viakoo. “The shift of ransomware to operations systems increased by 57% last year, and that trend is aggressively continuing.”
AI Rediscovers Industrial Security Flaws in Hours
Finite State tested its AI-driven analysis workflow against a vulnerable version of the AK-SM 800A firmware without telling it what flaws to look for. Working from the compiled software alone, the tool independently rediscovered two of three previously disclosed vulnerabilities within hours, according to the company.
The first was an authentication bypass that could let an attacker gain access without valid credentials. The second was a command-injection flaw that could allow unauthorized commands to run on the controller. Together, the vulnerabilities could potentially give an attacker control over refrigeration settings, including the ability to force defrost cycles or disable temperature alarms.
Finite State said it confirmed the command-injection flaw through laboratory testing and verified the authentication bypass through code analysis. It did not demonstrate a complete remote attack, however, and there is no evidence that these particular vulnerabilities were exploited in the French supermarkets.
The experiment nevertheless points to a potential shift in industrial cybersecurity. Analyzing compiled firmware has traditionally required specialized reverse-engineering expertise and considerable time. AI-assisted tools could make that work faster and more accessible, potentially reducing the time between the release of vulnerable firmware and the discovery of exploitable weaknesses.
Why Industrial Security Struggles to Keep Pace
Finding vulnerabilities is one thing. Fixing them is another, especially in operational technology (OT) environments where equipment can remain in service for decades. Unlike conventional IT systems, refrigeration controllers aren't necessarily easy to update. Installing new firmware may require coordination among equipment manufacturers, service contractors, and store operators, sometimes including an on-site visit.
That becomes particularly difficult for businesses managing hundreds of locations, each with its own equipment and maintenance requirements. Without a centralized way to track firmware versions and apply updates, vulnerable systems can remain in service long after fixes become available.
“Organizations who have no automated mechanism to enforce firmware updates, rotate credentials, and fix configuration drift on Ot/IoT assets across hundreds of remote sites are going to remain highly vulnerable to such attacks,” Gallagher said.
The problem gets harder when equipment reaches end of life. Without vendor support, operators may have no security patches to install, leaving them to replace otherwise functional hardware or find ways to protect it. AI-assisted vulnerability discovery threatens to widen the gap between how quickly weaknesses can be found and how quickly they can be addressed.
The implications extend beyond supermarkets. Similar refrigeration systems are used to store pharmaceuticals, vaccines, and other temperature-sensitive products. A compromised controller in those settings could destroy expensive inventory or disrupt supplies of medicines that depend on carefully maintained temperatures.
Reducing Exposure While Closing the Remediation Gap
"Organizations need to adopt an 'assume breach, assume vulnerable' approach to OT security," said Louis Eichenbaum, federal CTO at ColorTokens. "That starts with knowing exactly which operational assets exist, understanding their communications and dependencies, and eliminating unnecessary internet exposure. But visibility alone is not enough. Organizations must also implement granular microsegmentation and least-privilege access controls that restrict which systems and users can communicate with critical controllers."
For equipment that still receives security updates, operators should prioritize installing the latest firmware. Unsupported controllers need a replacement plan, with network isolation and restricted remote access providing protection in the meantime.
Those safeguards can also limit the damage from a breach elsewhere on the network. Compromising a workstation or remote access service shouldn't automatically give an attacker access to other operational systems.